
Vornin
Start free

Cybersecurity every company can run, and prove

Threats are probabilistic, so security runs on risk. Compliance needs proof, so the record demands rules. Vornin uses both: rules wherever the answer must be the same every time, AI wherever pattern recognition and context improve the outcome.

The Vornin story

Built from the audits we sat through

We ran IT operations for large corporations across international markets. It taught us that security is never 100%. The job is to cut the risk that matters most, every week.

The audits taught us the other half. An auditor does not accept “probably”. They want proof that holds up every time someone checks it.

The tools available were fragmented, split across vendors, sales calls and long rollouts. We wanted security and compliance as one workstream, with rules at the base and AI on top. So we built Vornin.

Created and hosted in the EU.

Why now

More vulnerabilities than any team can fix

AI speeds up attackers. Vulnerabilities now arrive faster than any team can patch them. Fixing everything is over. Fixing what matters first is the job.

AI works for defenders too. The best public threat intelligence combines machine learning with expert research to show which flaws attackers exploit now and which they will exploit next. We apply it by rule, so the same signal always gets the same answer.

  • Point in time

    Consultancies sell point-in-time assessments on a calendar, quarterly at best, at prices few companies can sustain.

  • Black box

    AI pentest tools are often a general-purpose model in a wrapper: it predicts the likely next step from its training data, with nothing deterministic underneath and nothing the customer can inspect.

  • Noise

    Legacy scanners run continuously but bury the signal in noise, behind opaque pricing, and leave the evidence to a separate GRC tool.

Vornin runs continuously and keeps the proof as it goes.

What we commit to

Three principles you can hold us to

  1. 01

    The record changes only by an explicit rule or a verified rescan

    As AI advances, our standard of proof stays fixed.

  2. 02

    One finding, one record, for its whole life

    Every change is recorded in a tamper-evident audit trail.

  3. 03

    Risk sets the order

    Severity alone says little. What attackers already exploit is never deprioritised.

The team

Who's behind Vornin

How we build
“Every feature starts with a problem: what an attacker can exploit, or what an auditor needs to see. Then we pick the right method and tool for the job, rules and AI together. Function over hype.”
Mathias Gatz and Thomas Freiesleben, co-founders
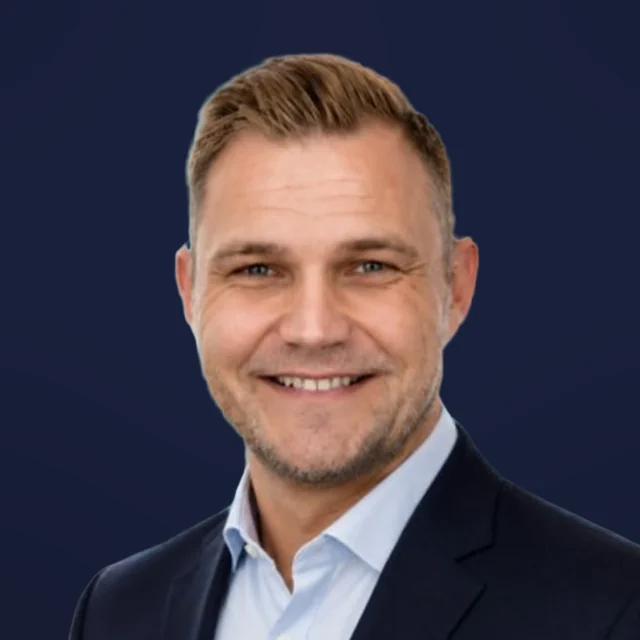
Mathias Gatz, co-founder and CTO

Mathias Gatz

Co-founder & CTO

Developer turned IT director. Runs security and compliance across 15+ countries and owns the IT audits: ISO 27001, GDPR, TISAX.

“Vornin is the platform I needed and couldn't find, so I built it. Now I use it to run security and compliance as one workflow and walk into audits with the evidence already built.”

Connect on LinkedIn
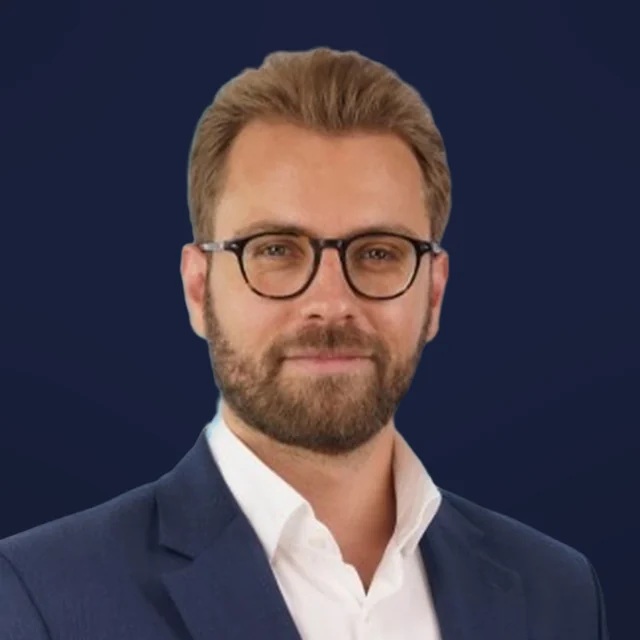
Thomas Freiesleben, co-founder and CMO

Thomas Freiesleben

Co-founder & CMO

Leads Vornin's commercial side. EXIN Information Security Foundation certified (ISO/IEC 27001).

“IT security and compliance should be easy to do and easy to buy. We built Vornin to open up a market still hidden behind unclear pricing, mandatory sales calls, and costly add-ons.”

Connect on LinkedIn

Vornin ApS Copenhagen, Denmark CVR 46625749 VAT DK46625749 Founded 6 July 2026

Start here

Run it on your own
attack surface

Start a free scan in minutes, or talk to us first.

Read-only access Working scan data deleted after each scan EU data residency