
Walk into your NIS2 audit with the evidence already built
Article 21 requires regular, documented vulnerability management, not a scan you run the week before the audit. Vornin maps every finding to the NIS2 measure it touches at scan time, tracks remediation against an SLA, and seals the record in a tamper-evident chain your auditor can verify.
Read-only access Working scan data deleted after each scan EU-hosted
NIS2 is the law.NIS2 is an EU directive. Direct obligations depend on national law and whether your organisation is in scope. Customers may request supplier evidence regardless. The evidence is on you
NIS2 duties depend on national law and scope. Suppliers can face customer security and evidence requests.
Not sure if you're in scope, or what non-compliance actually costs? Read the full NIS2 compliance guide →
Article 21 measures, mapped to what the auditor sees
Every finding auto-links to the NIS2 measure it touches at the moment it is ingested. This is the cross-walk from the law to the evidence Vornin produces for it.
| NIS2 Article 21(2) measure | What Vornin runs | Evidence it produces |
|---|---|---|
| Art. 21(2)(e)Vulnerability handling and disclosure | Scheduled scanning of web apps, APIs, networks, code and containers, with deduplication and SLA-tracked remediation. | Per-finding auditor pack ZIP carrying the full detect-to-resolved lifecycle. |
| Art. 21(2)(i)Asset management | Continuous attack surface discovery checks for new subdomains daily and records the services, certificates and technologies your scans detect. | Asset inventory that never silently drops a tracked host. |
| Art. 21(2)(d)Supply-chain security | Dependency scanning with reachability ranking, plus a CycloneDX software bill of materials. | SBOM.cdx.json export and SCA findings mapped to the control. |
| Art. 21(2)(h)Cryptography and encryption | SSL/TLS scanning for weak ciphers, deprecated protocols, expiring certificates, and missing HSTS. | Encryption findings with severity and remediation deadlines. |
| Art. 21(2)(f)Effectiveness of the measures | Live per-framework compliance score, a 90-day trend, and a coverage-gap report naming untested controls. | Score export plus the gap report, so the number stays honest. |
| Art. 21(2)(a)Risk analysis | Severity, exploit likelihood, and reachability combined into a single prioritised view across every finding. | Ranked risk view that shows what to fix first, with the reasoning recorded. |
Governance, business continuity, and cyber hygiene and training controls cannot be proven by a scanner. Vornin tracks them through the manual attestation workflow with sign-off history and excludes them from the auto-tested score, so your coverage number reflects what was actually verified. Read the NIS2 vs ISO 27001 comparison →
Evidence your auditor can verify themselves
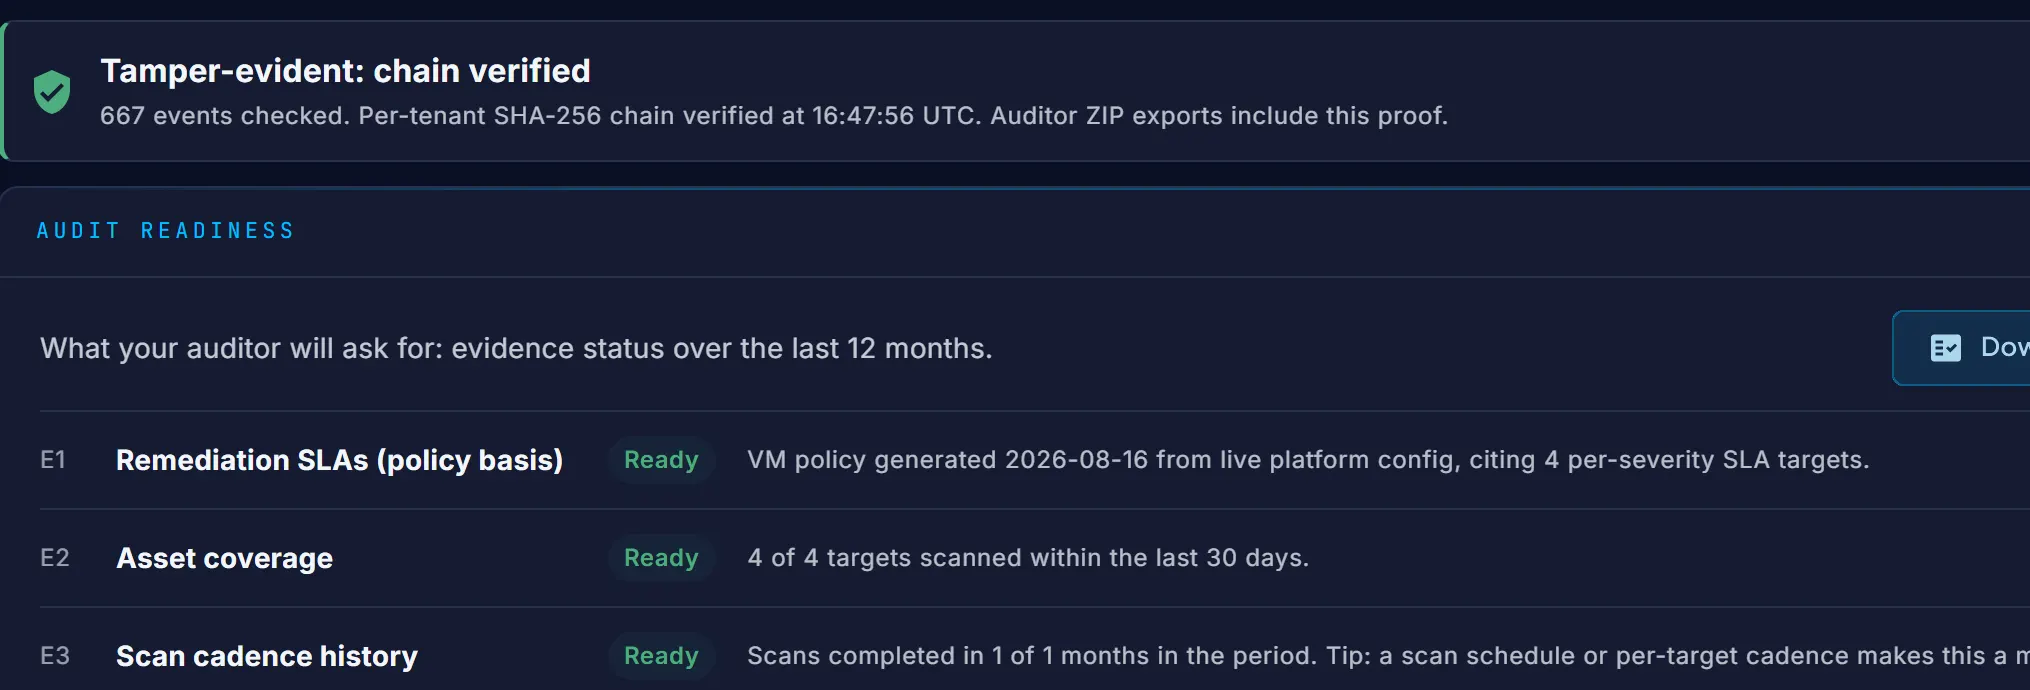
Give your auditor finding history and remediation evidence together. Tamper-evident records with SHA-256 verification make integrity checks part of the review, alongside the evidence that a fix was confirmed.
- Chain
SHA-256 verification
Review status changes in a tamper-evident history with SHA-256 verification. Give your auditor a record to check alongside the remediation evidence.
- Log
Consistent finding history
Review finding updates in one tamper-evident record, ready for your next audit.
- Verify
Verify on demandChain verification checks recorded history for tampering. Review the remediation evidence alongside it to assess whether a vulnerability was fixed.
Run history verification on demand and include the result in the auditor pack. Your assessor can review the integrity check alongside the finding evidence.
Per-finding ZIP, tenant-wide PDF
Export a ZIP with finding history, comments, compliance mappings, and evidence, or a PDF for the whole estate. Both exports are available on Business and Scale.
NIS2, answered
The questions that come up most when an IT manager first reads Article 21.
Does NIS2 apply to my company?
NIS2 covers 18 sectors, including energy, transport, banking, health, digital infrastructure, manufacturing, and public administration. It generally covers medium-sized and larger organisations, with exceptions for smaller entities. Check national law and the size and sector rules. Suppliers can face contractual security and evidence requests without being directly in scope.
What evidence do NIS2 auditors ask for?
An auditor wants proof that vulnerability management runs as a documented process, not a one-off scan: regular scanning, assigned remediation, SLA tracking, and confirmation that findings were closed. They also want assurance the records were not edited after the fact. Vornin produces this as a per-finding auditor pack with a tamper-evident chain verification result baked in.
What does Article 21 require for vulnerability management?
Article 21(2) lists risk-management measures including vulnerability handling and disclosure (e), asset management (i), supply-chain security (d), and cryptography (h). Vornin runs scanner coverage against each of these and maps every finding to the control it touches at scan time. Read the full NIS2 compliance guide.
Is NIS2 the same as ISO 27001?
No. ISO 27001 is a voluntary standard you can certify against; NIS2 obligations follow national law. For Article 21 or 23 breaches, maximum fines must be at least €10 million or 2% of worldwide annual turnover for essential entities, and €7 million or 1.4% for important entities, whichever is higher. An ISO 27001 vulnerability management programme supports NIS2 work but does not establish compliance. Vornin maps findings to both.
Our customers are asking about our NIS2 posture. What do we show them?
NIS2 entities must secure their supply chain under Article 21(2)(d), so they push security questionnaires and proof-of-remediation requests down to suppliers, often before a deal closes. Hand them a per-finding auditor pack: scan, remediation, and confirmed closure, sealed in a tamper-evident chain. EU-hosted answers the data-residency line on the same questionnaire. Answer it instead of stalling the deal.
Tier note: the attestation workflow and evidence vault unlock on Team. The tamper-evident chain records finding history on every plan. Per-finding auditor ZIP and tenant-wide auditor PDF exports unlock on Business and Scale. Business includes evidence exports you can hand to an auditor. Compare tiers →
Start your NIS2 evidence trail today
Run a scan today and Vornin starts building your evidence trail. No setup fee, no sales call, no consultant.
Read-only access Working scan data deleted after each scan EU-hosted