
ISO 27001 audit prep with real evidence
An auditor needs a documented scan and remediation cycle operating over time, not a point-in-time report. Vornin maps every finding to the Annex A control it touches, keeps a tamper-evident lifecycle, and produces per-finding evidence packs your auditor can validate.
Read-only access Working scan data deleted after each scan EU-hosted
Certification is a cycle, not a snapshot
The stage 2 audit needs evidence that A.8.8 technical vulnerability management is operating. Surveillance audits need evidence it kept operating. Keep scan history, remediation records, and integrity checks ready.
Annex A controls, cross-walked to scanner evidence
Every finding auto-links to the Annex A control it touches the moment it is ingested. This is the cross-walk from the 2022 technological control set, plus A.5.23 for cloud services, to the evidence Vornin produces for your auditor.
9of 93
Annex A controls that Vornin supports with proof. The rest of Annex A is policy, people, physical and process work that your ISMS owns.
A.5Organizational2 of 37 mapped
- 5.1
- 5.2
- 5.3
- 5.4
- 5.5
- 5.6
- 5.7
- 5.8
- 5.9
- 5.10
- 5.11
- 5.12
- 5.13
- 5.14
- 5.15
- 5.16
- 5.17 Authentication information, supported with proof
- 5.18
- 5.19
- 5.20
- 5.21
- 5.22
- 5.23 Information security for use of cloud services, supported with proof
- 5.24
- 5.25
- 5.26
- 5.27
- 5.28
- 5.29
- 5.30
- 5.31
- 5.32
- 5.33
- 5.34
- 5.35
- 5.36
- 5.37
A.6People0 of 8 mapped
- 6.1
- 6.2
- 6.3
- 6.4
- 6.5
- 6.6
- 6.7
- 6.8
A.7Physical0 of 14 mapped
- 7.1
- 7.2
- 7.3
- 7.4
- 7.5
- 7.6
- 7.7
- 7.8
- 7.9
- 7.10
- 7.11
- 7.12
- 7.13
- 7.14
A.8Technological7 of 34 mapped
- 8.1
- 8.2
- 8.3
- 8.4
- 8.5
- 8.6
- 8.7
- 8.8 Management of technical vulnerabilities, supported with proof
- 8.9 Configuration management, supported with proof
- 8.10
- 8.11
- 8.12
- 8.13
- 8.14
- 8.15
- 8.16
- 8.17
- 8.18
- 8.19
- 8.20 Networks security, supported with proof
- 8.21
- 8.22
- 8.23
- 8.24 Use of cryptography, supported with proof
- 8.25 Secure development life cycle, supported with proof
- 8.26
- 8.27 Secure system architecture and engineering principles, supported with proof
- 8.28 Secure coding, supported with proof
- 8.29
- 8.30
- 8.31
- 8.32
- 8.33
- 8.34
Controls a scanner cannot test stay outside the auto-tested score, so the coverage number reflects what scans verified. A.5.23 counts on cloud posture findings, which support the control but do not replace your cloud-service processes. What a vulnerability scan actually checks →
| ISO 27001:2022 Annex A control | What Vornin runs | Evidence it produces |
|---|---|---|
| A.8.8Management of technical vulnerabilities | Scheduled scanning of web apps, APIs, networks, code and containers, with deduplication and SLA-tracked remediation. | Per-finding auditor pack ZIP carrying the full detect-to-resolved lifecycle. |
| A.8.20Networks security | Port and service discovery plus DNS security checks on a schedule. | Exposed-service and DNS findings mapped to the control, with remediation deadlines. |
| A.8.24Use of cryptography | SSL/TLS scanning for weak ciphers, deprecated protocols, expiring certificates, and missing HSTS. | Encryption findings with severity and remediation deadlines. |
| A.8.25 · A.8.28Secure development and coding | Static analysis on connected repositories, plus web application and API testing. | Code and application findings mapped to the control, with the lifecycle recorded. |
| A.8.9 · A.5.23Configuration management and cloud services | Cloud posture checks across AWS, Azure and Google Cloud, plus infrastructure-as-code scanning. | Misconfiguration findings mapped to the control and tracked to closure. For A.5.23, this is supporting evidence alongside your cloud-service processes. |
One evidence layer for every audit in the cycle
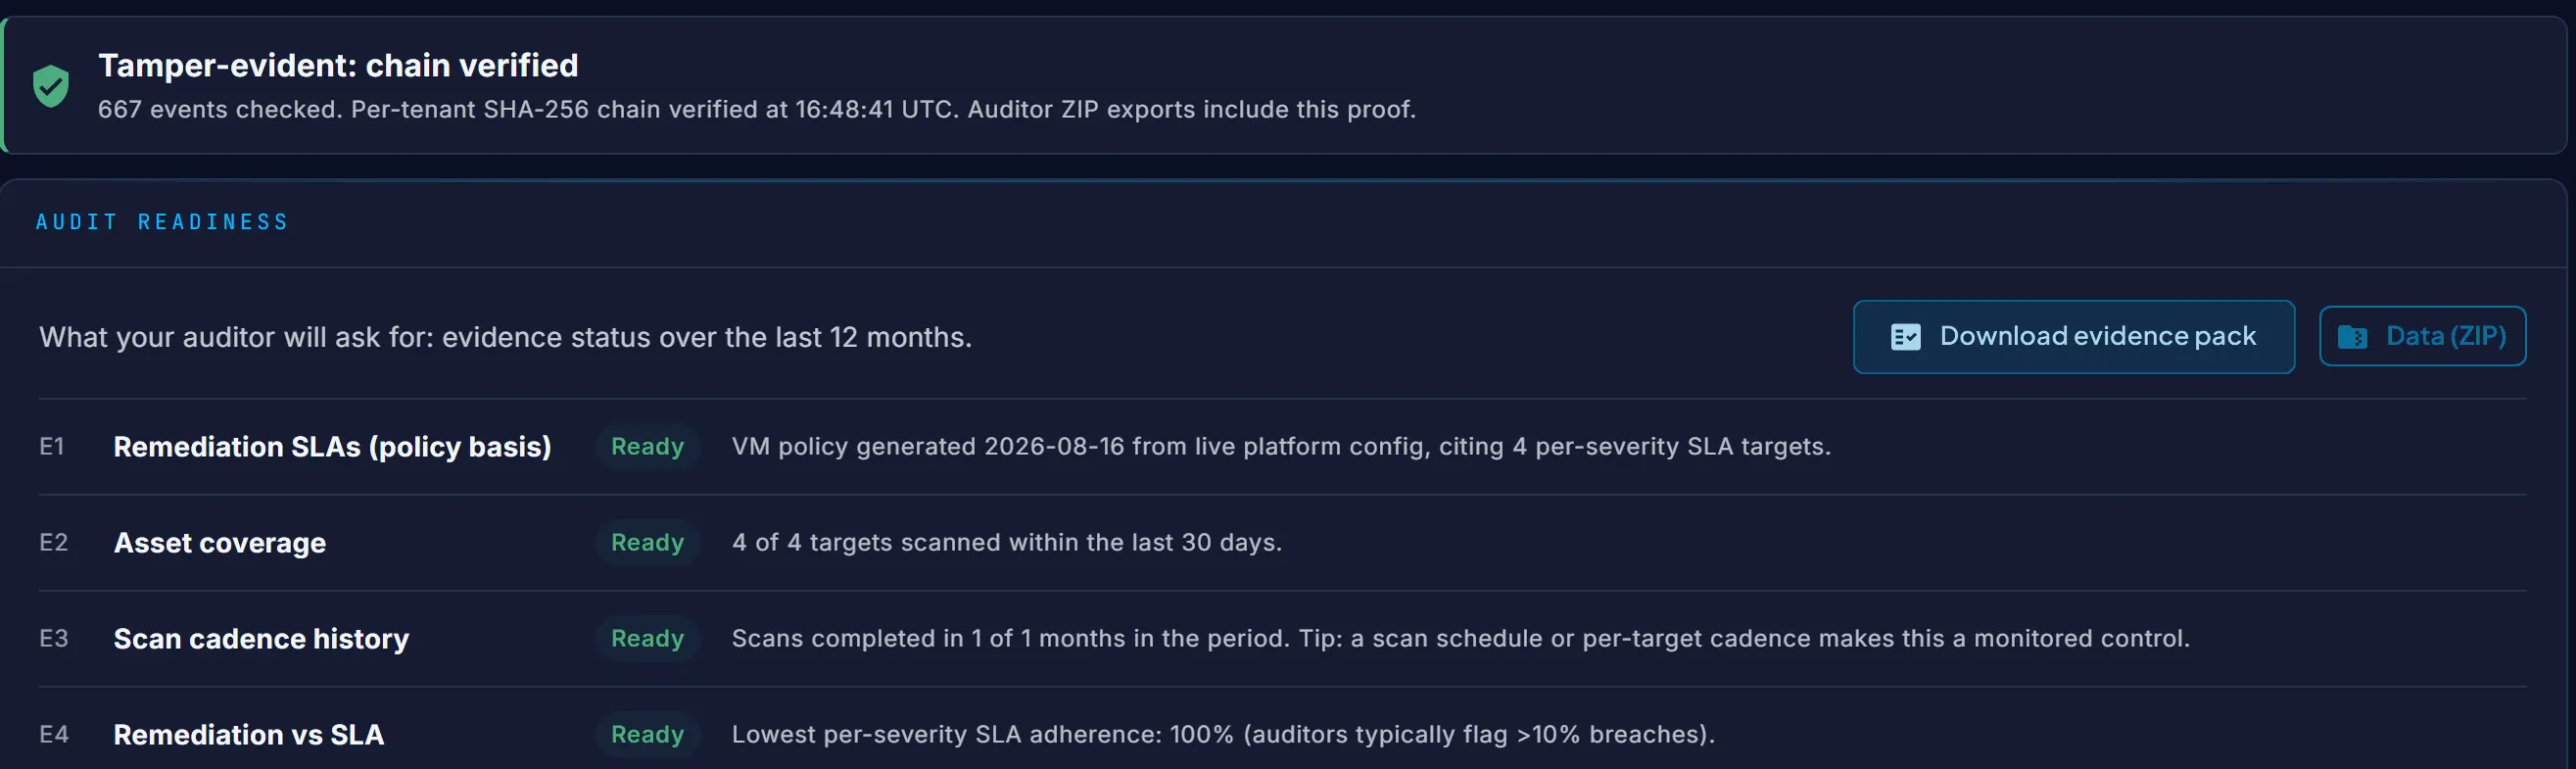
The chain records every status change as it happens, so the evidence for stage 2, surveillance, and recertification already exists when each audit lands.
- Chain
SHA-256 verification
Review status changes in a tamper-evident history with SHA-256 verification. Give your auditor a record to check alongside the remediation evidence.
- Log
Consistent finding history
Review finding updates in one tamper-evident record, ready for your next audit.
- Verify
Verify on demandChain verification checks recorded history for tampering. Review the remediation evidence alongside it to assess whether a vulnerability was fixed.
Run history verification on demand and include the result in the auditor pack. Your assessor can review the integrity check alongside the finding evidence.
Per-finding ZIP, tenant-wide PDF
Export a ZIP with finding history, comments, compliance mappings, and evidence, or a PDF for the whole estate. Both exports are available on Business and Scale.
ISO 27001, answered
The questions that come up most when a team scopes the technical-vulnerability control.
Does ISO 27001 require vulnerability scanning?
Yes, in practice. Annex A control A.8.8, management of technical vulnerabilities, requires that information about technical vulnerabilities is obtained, exposure evaluated, and appropriate measures taken. An auditor expects evidence of regular scanning, evaluation, and remediation, not a single point-in-time report. Vornin runs the scanning and records the full lifecycle as that evidence.
Which Annex A controls cover vulnerability scanning?
The primary control is A.8.8 (management of technical vulnerabilities). Vornin also maps findings to A.8.20 (networks security), A.8.24 (use of cryptography), A.8.25 and A.8.28 (secure development and coding), A.8.9 (configuration management), A.8.27 (secure system architecture), A.5.17 (authentication information), and A.5.23 (cloud services). Each finding maps to the Annex A control it touches at scan time.
What evidence does an ISO 27001 auditor want?
An auditor wants to see the control operating over time: a documented scan cadence, evaluated findings, assigned remediation with deadlines, and confirmed closure. They want a lifecycle trail, not just a scan result. Vornin produces a per-finding auditor pack covering detection through resolution, with a tamper-evident chain so the records cannot be quietly edited before the audit.
Does Vornin help with annual surveillance audits?
Yes. Certification runs on a three-year cycle: surveillance audits in years one and two, recertification in year three. Because Vornin keeps scanning continuously and records every status change, the evidence for each surveillance audit already exists. You export the auditor pack or per-framework mapping table instead of reconstructing a year of activity.
Is ISO 27001 the same as NIS2?
No. ISO 27001 is a voluntary standard you can certify against; NIS2 obligations follow national law. Their controls overlap, so vulnerability management records can support both; see NIS2 vs ISO 27001 for how the two frameworks differ. Vornin maps findings to ISO 27001 and NIS2, but mapping does not establish compliance.
Tier note: the tamper-evident chain records finding history on every plan. Per-finding auditor ZIP and tenant-wide auditor PDF exports unlock on Business and Scale. Compare tiers →
Build your ISO 27001 evidence file continuously
Start now and the evidence file is already there when the next audit lands.
Read-only access Working scan data deleted after each scan EU-hosted