
Cybersecurity with less noise and more verified fixes
You own the infrastructure and the compliance risk. Risk-based vulnerability management ranks findings by exploitation and reachability, merges duplicates, and closes a finding only when a rescan no longer detects it. Findings map to controls across nine frameworks, including NIS2, DORA, and ISO 27001.
Read-only access Working scan data deleted after each scan EU-hosted
You carry security, on top of everything else
You keep the systems running securely and fix vulnerabilities as they pop up. Then NIS2 hits, the board wants a posture slide, and customer security questionnaires start arriving. The same issue shows up in three tools, and triage becomes reconciliation instead of risk-based prioritization. You need ranked findings and fixes you can prove, not another tool to babysit.
Read what NIS2 compliance requires before the letter lands →
Fewer tools to manage, easier to report on progress
One login and one bill replace the scanning stack. Scans run on schedule, every finding follows the same vulnerability management lifecycle, and reports go to leadership and audit review without reformatting. Published pricing lets you assess the cost before committing.
See how the vulnerability management workflow takes a finding from scan to verified fix →
- Consolidate
One platform, not five tools
Replace the OpenVAS, Nmap, and ad-hoc web-scanner stack with a single platform across your attack surface, web apps, APIs, networks, code, containers and cloud. One login, one bill, one finding inbox.
- Prioritise
One finding per issue, ranked by risk
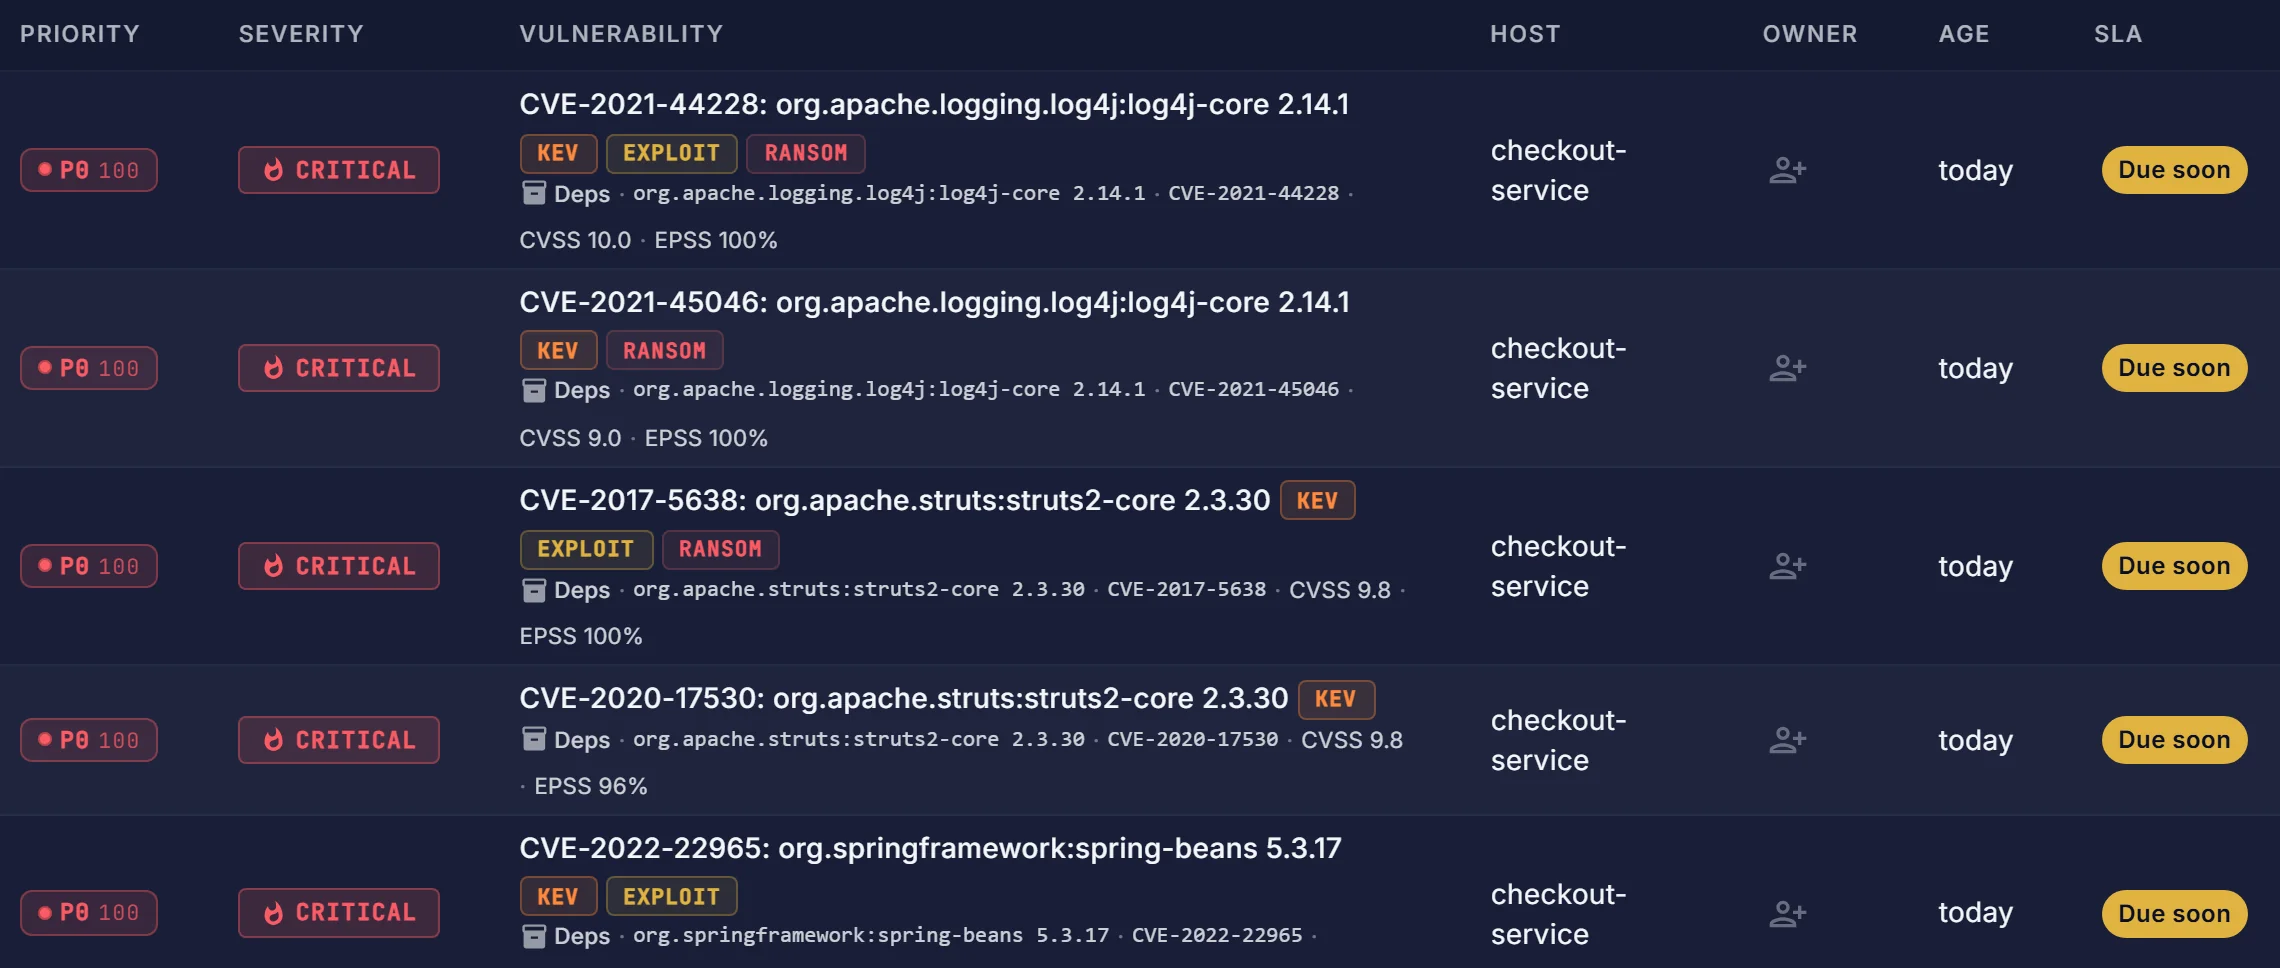
The same issue found by several scans or on several URLs becomes one finding, and an upgrade that fixes six CVEs shows as one row. Priority bands from CVSS, EPSS, CISA KEV and reachability rank the rest. Actively exploited issues are never pushed down.
- Verify
Fixes confirmed, not assumed
Re-test a network finding on demand, and the confirmed fix is recorded as verified in the evidence trail. Every status change records who did what and when, so the history holds up when someone asks.
- Accountable
SLAs you can stand behind
Assign findings to owners with reminders, and set remediation deadlines per severity. On Business and above, escalation emails fire when one slips. A 30-day rolling MTTR gives you the number to show when leadership asks if it is under control.
- Report
Reports leadership actually reads
One scan produces a technical report for you and an executive brief for the board, on your branding from Business up. No manual reformatting the night before the meeting.
- Hands-off
Scheduled scans that just run
Set the scan schedule once and review findings as they arrive. Incomplete scans are flagged, so missing coverage is visible alongside the results.
- Budget
A price you can self-authorise
Published per-target pricing, self-serve checkout below Scale, and by-request onboarding for Scale. You know the cost before you commit, and it scales by targets, not seats.
- Sovereignty
The answer to the data question
EU data residency, read-only target access, and working scan data deleted after scanning. When the CTO or a customer asks what the tool sees and where the data goes, the answer is already on record.
Compare the full feature set →
Cut the noise, prove the fix
Free includes web and network scanning and a framework preview. Paid plans and the 14-day Business trial add code and cloud, no credit card required.
Read-only access Working scan data deleted after each scan EU-hosted