
Vornin connects attack-surface monitoring, scanning, fix tracking, reporting and compliance evidence in one EU-hosted vulnerability management platform.
Vornin vs HostedScan
HostedScan is built for vulnerability scanning. Vornin runs the whole vulnerability lifecycle, from scan to verified fix, with evidence for technical security controls. HostedScan offers endpoint agents on higher plans, plus a lower entry price.
Vornin as a HostedScan alternative, at a glance
Both offer self-serve network, web application and API scanning with public pricing. Vornin also scans code, containers, Kubernetes and cloud configuration in an EU-hosted platform.
| Criterion |  |
HostedScan |
|---|---|---|
| Data residency | EU-hosted | US-hosted; no EU hosting option |
| Built-in scanning coverage |
|
|
| Compliance support |
|
|
| Remediation and evidence |
|
|
| Internal scanning |
|
|
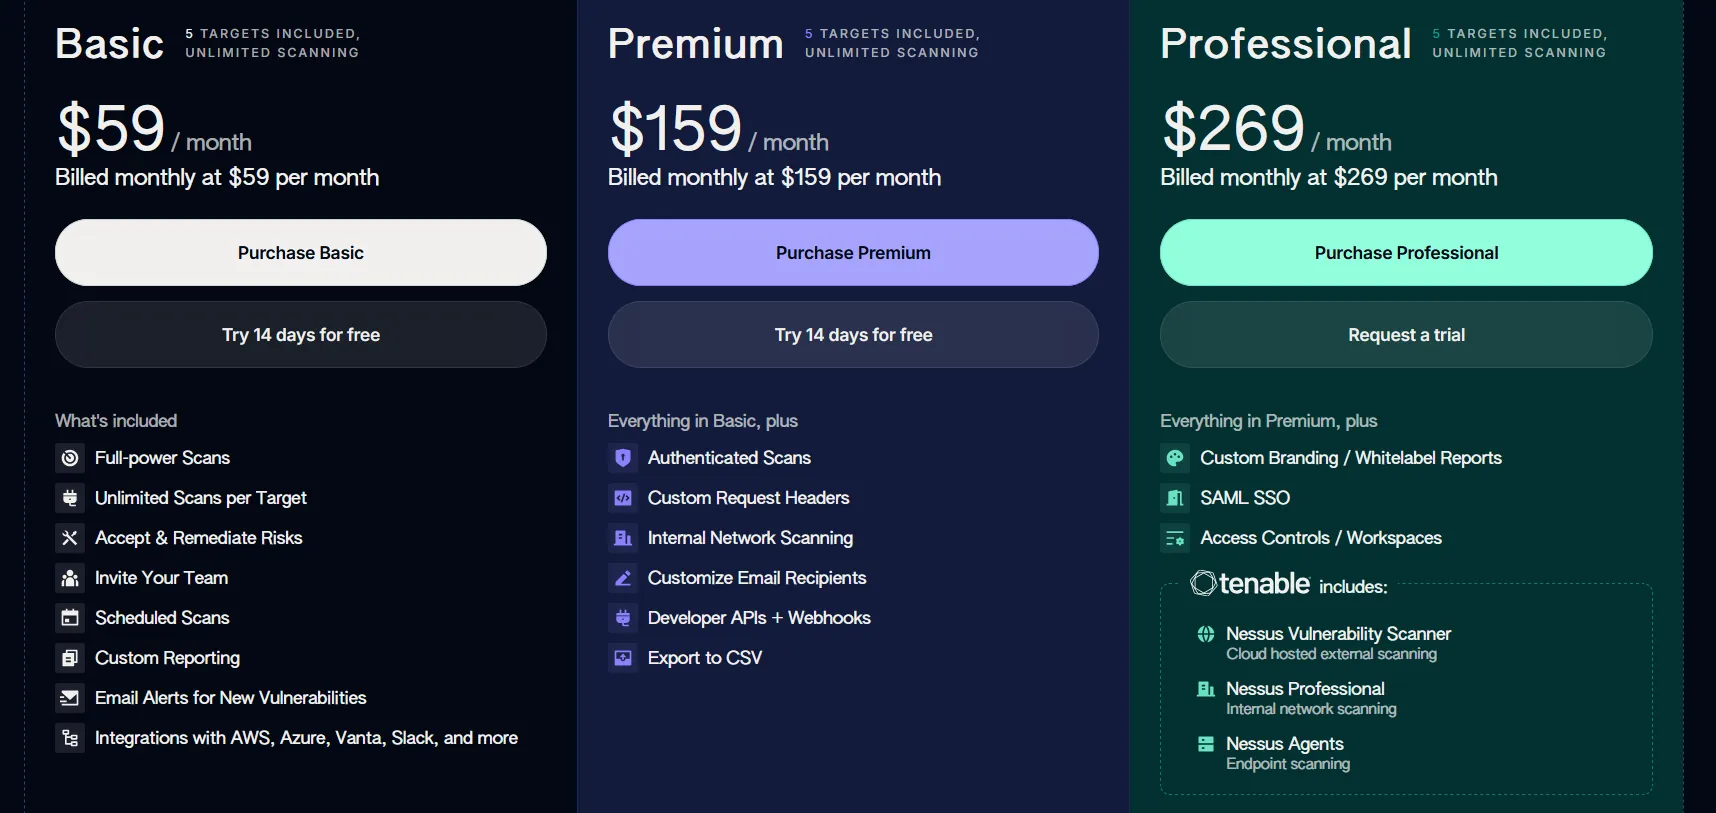
| Comparable monthly cost | €129/month | $159/month |
Prices cover five targets with authenticated web and internal network scanning, excluding tax. Currencies and included features differ.
How each platform handles vulnerability management
HostedScan
HostedScan combines established network and web scanners with attack-surface monitoring, scheduled scans, reports and team access.
- Scan Vornin: Network, web, code and cloud HostedScan: Network, web and API
- Prioritise Vornin: CVSS, EPSS, CISA KEV HostedScan: CVSS and EPSS
- Assign Vornin: Finding owners HostedScan: Team access (partial)
- Deadlines Vornin: SLA with escalation HostedScan: No SLA deadlines
- Verify fix Vornin: Rescans verify fixes HostedScan: Closes on rescan
- Evidence Vornin: Mapped to compliance controls HostedScan: PDF reports (partial)
What five targets cost to scan
Five targets, authenticated web scans and internal network scanning: €129/month with Vornin or $159/month with HostedScan.
| Platform | Monthly price | Included in this comparison |
|---|---|---|
|
€129 |
|
| HostedScan | $159 |
|
Monthly list prices, excluding tax. Feature availability and quotas vary by subscription; additional capabilities may cost more.
- External scanning
- Internal network
- Code
- Dependencies
- Secrets
- Containers
- Kubernetes
- Cloud configuration
- Endpoint agents (not included)
HostedScan
- External scanning
- Internal network
- Endpoint agents on higher plans
- Greenbone Enterprise add-on
Results imported via Snyk, Dependabot or API
Third-party tools HostedScan needs for the same coverage Not included
- Code
- Dependencies
- Secrets
- Containers
- Kubernetes
- Cloud configuration
Integrations and stack coverage
Vornin includes code, container and cloud scanning in the price shown. With HostedScan, factor in any licences and the work of running the separate tools that cover them, plus the Greenbone Enterprise add-on if you need it.
Reporting and audit evidence
Both provide custom reports, PDF reports and CSV exports. Vornin offers executive, technical, auditor and scan-comparison reports, scoped to selected assets or groups, with scheduled delivery.
Licensing and pricing as you grow
Both charge by target. HostedScan has lower extra-target rates; compare total costs using both pricing calculators.
Choose for your scanning and compliance needs
Choose if
- You need a vulnerability management programme, not just a scanner, with evidence for your IT audit and ISMS.
- You need to show an auditor, regulator or customer what was found and fixed.
- You need EU data residency.
- You need a persistent finding record from discovery to verified fix, with owners, deadlines and decisions kept together.
- You want code, container, Kubernetes and cloud findings alongside network and web findings, without a second scanning tool.
Choose HostedScan if
- You only need external network, web application and API scanning. HostedScan starts at $59/month; code, container and cloud-configuration scans require separate tools.
- You need Greenbone's commercial detection feed for Exchange, Palo Alto, Cisco or IoT/OT equipment. HostedScan sells it as an add-on.
- You need endpoint agents and do not already run one such as Microsoft Defender. HostedScan offers Nessus Agents; Vornin has no endpoint agent.
Scan coverage and workflow
- Attack-surface monitoring
- Network and ports
- Web apps and APIs
- SSL/TLS
- DNS and email
- Subdomains
- Source code
- Dependencies
- Secrets
- Infrastructure as code
- Containers
- Kubernetes
- Cloud configuration
- Internal network
- Endpoints (not included)
HostedScan
- Attack-surface monitoring
- Network and ports
- Web apps and APIs
- SSL/TLS
- DNS and email (partial)
- Subdomains
- Source code (not included)
- Dependencies (not included)
- Secrets (not included)
- Infrastructure as code (not included)
- Containers (not included)
- Kubernetes (not included)
- Cloud configuration (not included)
- Internal network
- Endpoints
| Capability | |
HostedScan |
|---|---|---|
| Scanning | ||
| Attack-surface monitoring | Yes | Yes |
| Network and port scanning | Yes | Yes |
| Web app and API scanning | Yes, including authenticated scans | Yes, including authenticated scans |
| SSL/TLS | Yes | Yes |
| DNS and email security | Yes | Standalone SPF, DKIM and DMARC checker only |
| Subdomain discovery and takeover | Yes | Yes |
| Source code (SAST) | Yes | No |
| Dependencies (SCA) | Yes | No; imports Snyk or Dependabot results |
| Secrets in code | Yes | No |
| Infrastructure as code | Yes | No |
| Container images | Yes | No; imports Snyk results |
| Kubernetes | Yes | No |
| Cloud configuration | Yes, AWS, Azure and Google Cloud | No; cloud sync adds scan targets only |
| Internal network scanning | Yes, through an on-premise agent | Yes, through an internal scanner |
| Endpoint agents | No | Yes, Nessus Agents |
| Prioritisation and remediation | ||
| Risk-based prioritisation | CVSS, EPSS, CISA KEV (known exploited vulnerabilities) and dependency reachability | CVSS and EPSS scoring; target health scores |
| Ownership and risk decisions | Finding owners; risk acceptance with approval and review dates | Team access and risk acceptance rules |
| Findings deduplicated across scanners | Yes | No |
| SLA deadlines and escalation | Yes, with automatic escalation | No |
| Engineering integrations | Issue creation in Jira Cloud, GitHub, GitLab and Azure DevOps; API and webhooks | API, webhooks and cloud-target sync; no built-in ticketing integration |
| Reporting and compliance evidence | ||
| Custom reports, PDF reports and CSV exports | Yes; executive, technical, auditor and scan-comparison reports | Yes; per-scan reports and executive summaries |
| Findings mapped to compliance controls | Yes, nine frameworks, including SOC 2, ISO 27001, GDPR, NIS2 and DORA | No |
| Tamper-evident finding history | Yes | No |
| Auditor evidence pack | Yes, evidence packs scoped to an audit period | No audit-trail evidence pack; PDF reports available |
| Data residency | ||
| Hosting | EU | US |
IncludedNot includedPartial
Imports require output from separate tools, such as Snyk or Dependabot, in addition to using HostedScan. Feature access varies by subscription.
Compare audit evidence, data residency and fix tracking
Evidence you can hand an auditor
- Custom reports, PDF reports and CSV exports; executive, technical, auditor and scan-comparison views
- Custom reports scoped to selected assets or groups, with white-label options
- Finding history mapped to nine compliance frameworks, with tamper-evident records
- Audit-readiness checks, manual attestations and period-scoped evidence packs
HostedScan
- Custom reports, PDF reports and CSV exports; per-scan views and executive summaries
- Custom reports with white-label options
- No finding-to-control mapping or tamper-evident history
- No audit-trail evidence pack
For an audit or customer security questionnaire, compare the evidence you can deliver. Tamper-evident history makes later record changes detectable.
EU jurisdiction and data residency
- European company with no US office or parent, outside US CLOUD Act jurisdiction
- Scan results, findings and audit evidence stored in the EU under EU law
HostedScan
- US company storing account data, scan results and reports in the US
- No EU hosting option; EU transfers use Standard Contractual Clauses
Tip: Check both data location and legal jurisdiction against procurement requirements.
Coverage across attack vectors
- Attack surface, network, web application and API scanning
- Built-in scanning for source code, dependencies, secrets, infrastructure as code, containers, Kubernetes and cloud configuration
- Internal network scanning through a customer agent; no endpoint agents
HostedScan
- Attack surface, network, web application and API scanning
- Dependency and container findings imported from tools such as Snyk and Dependabot (partial)
- Internal network scanning and Nessus endpoint agents
Vornin includes more scan surfaces in one platform. HostedScan adds endpoint coverage and can import findings from separate tools.
From finding to verified fix
- Keep a persistent finding record across scans, with owners, deadlines and risk decisions
- Track deadlines and escalate overdue work
- Successful rescans verify fixes; manual closures and accepted risks remain distinct
- Create issues in Jira Cloud, GitHub, GitLab and Azure DevOps
HostedScan
- Track risks across scans and close findings when later scans no longer detect them
- No SLA deadlines or escalation
- Accept risks using rules; automate scans and results through APIs and webhooks
- No built-in issue creation in Jira, GitHub, GitLab or Azure DevOps
Compare how work is assigned, how deadlines are enforced and what remains as proof after a fix.
HostedScan comparison FAQ
Is Vornin a HostedScan alternative?
Yes. Vornin offers self-serve vulnerability management with EU hosting, compliance mapping and code and cloud scanning. HostedScan is stronger when you need Nessus endpoint agents or its Greenbone Enterprise add-on.
What is the main difference between Vornin and HostedScan?
Vornin is a vulnerability management platform; HostedScan is built around vulnerability scanning. Vornin has more scan surfaces built in, including code, containers and cloud, ranks findings by known exploitation (CISA KEV), EPSS and reachability, tracks remediation against SLA deadlines, verifies fixes and maps findings to compliance controls, all EU-hosted. HostedScan offers endpoint agents on higher plans, plus a lower entry price.
When is HostedScan better than Vornin?
HostedScan fits better when you need:
- Nessus endpoint agents
- The Greenbone Enterprise detection feed, sold separately
- External network, web application and API scanning from $59/month, with code, container and cloud-configuration scans handled by separate tools
Comparison details
Source: HostedScan's public website. Last verified .
Comparison based on public documentation, not hands-on testing. Vornin is not affiliated with HostedScan.
Vulnerability management with audit evidence
Start with a free scan. Paid plans use public, target-based pricing.
Read-only access Working scan data deleted after each scan EU-hosted