The Tenable alternative for lean IT and security teams
Vornin scans networks and web apps like Tenable, plus source code, and includes the containers and cloud Tenable prices on request. Vornin simplifies vulnerability management with owner assignment, SLA deadlines with auto-escalation and audit evidence for compliance controls. Vornin costs 34% less for 100 hosts and five web apps, with data EU-hosted under EU jurisdiction.
Bottom line: Tenable's published prices cover networks and web apps. Tenable charges extra for attack surface management (ASM), containers, Kubernetes clusters and cloud and does not scan source code, dependencies or secrets in code. Vornin includes all of them and lets you assign ownership to each finding, with SLA deadlines, auto-escalation and notifications, plus NIS2 and DORA evidence. Vornin costs 34% less for 100 hosts and five web apps and keeps findings under EU jurisdiction, where Tenable is a US company hosting on US-owned AWS.
Against Tenable, Vornin adds code, container, Kubernetes cluster and cloud scanning to the same subscription as your network scans. Tenable does not escalate a missed deadline and bills annually only.
Criterion
Tenable
Scanning coverage
Internal and external networks and TLS: Yes
Web apps and APIs: Yes
Attack surface and subdomains: Yes
DNS and email: Yes
Code, dependencies and secrets in code: Yes
Infrastructure as code, containers, Kubernetes clusters and cloud configuration: Yes
Internal and external networks and TLS: Yes
Web apps and APIs: Yes, on a separate licence
Attack surface and subdomains: Yes, on quote
DNS and email: Partial
Code, dependencies and secrets in code: No
Infrastructure as code, containers, Kubernetes clusters and cloud configuration: Yes, on quote
Compliance evidence
Findings mapped to compliance controls: Yes, nine frameworks
Tamper-evident finding history: Yes
Auditor evidence pack: Yes
Findings mapped to compliance controls: Partial, configuration audits only
Tamper-evident finding history: No
Auditor evidence pack: No
Remediation
Named owner per finding: Yes
Automatic escalation: Yes
Tickets in GitHub, GitLab or Azure DevOps: Yes
Named owner per finding: Partial, on the linked ticket
Automatic escalation: No
Tickets in GitHub, GitLab or Azure DevOps: No
Pricing model
An IP range or cloud account counts as one target
Web apps in the same plan as hosts
Monthly or annual billing
Every asset licensed, about €44.40 a year each
Web apps on a separate licence
Annual prepaid billing only
Data stored in the EU
Yes
Yes, Frankfurt region on US-owned AWS
Scan results and customer findings outside US CLOUD Act reach
Yes: hosting and AI with EU providers
No: US company on US-owned AWS
Comparable yearly cost
€7,092/year, €591/month on annual billing
€10,748.44/year, prepaid; €895.70/month computed
Prices cover 100 hosts and five web apps on Vornin Business, annual billing, and on Tenable One Vulnerability Management plus Tenable One Web App Scanning, annual prepaid, excluding VAT. Tenable's monthly figure is its annual price divided by 12. Included features differ.
How Tenable Nessus and Tenable One handle vulnerability management compared to Vornin
Bottom line: as a Nessus alternative, Vornin keeps internal and external network scanning and adds source code scanning, which Tenable does not offer, and the container and cloud scanning Tenable prices on request. You assign ownership to each finding, with SLA deadlines, auto-escalation, notifications and evidence mapped to compliance controls. Tenable puts the owner on the linked ticket, shows SLA deadlines in a dashboard widget and does not escalate.
Vornin scans your external attack surface and subdomains, web apps and APIs, internal and external networks, TLS, DNS and email security, code and secrets, dependencies, infrastructure as code, containers, Kubernetes and cloud posture on AWS, Azure and Google Cloud.
Assign finding owners, set SLA deadlines, and automate escalations and notifications, with compliance evidence in one vulnerability management platform and subscription.
Scan data, findings and AI processing stay with EU providers.
vs
Tenable
Tenable scans internal and external networks and TLS with Nessus Professional, software you install, and Tenable One Vulnerability Management, licensed per asset.
Web apps and APIs need a separate Web App Scanning licence, or Nessus Expert for five web apps per rolling 90 days. Tenable covers DNS and email security in part and prices ASM with subdomains, containers, Kubernetes, cloud posture and infrastructure as code on request.
Tenable does not scan code, secrets or dependencies, and its cloud data sits on US-owned AWS.
Tenable
ScanVornin: Attack surface, web apps, APIs, networks, code, containers and cloudTenable: Networks; web apps and APIs on a separate licence; ASM, containers and cloud on quote; no code (partial)
AssignVornin: Named owner per findingTenable: Owner on the linked ticket only (partial)
DeadlinesVornin: SLA deadlines with email and webhook escalationTenable: SLA widget only, no escalation (partial)
EvidenceVornin: Each finding mapped to controls, tamper-evidentTenable: Config audits only, no tamper-evident history (partial)
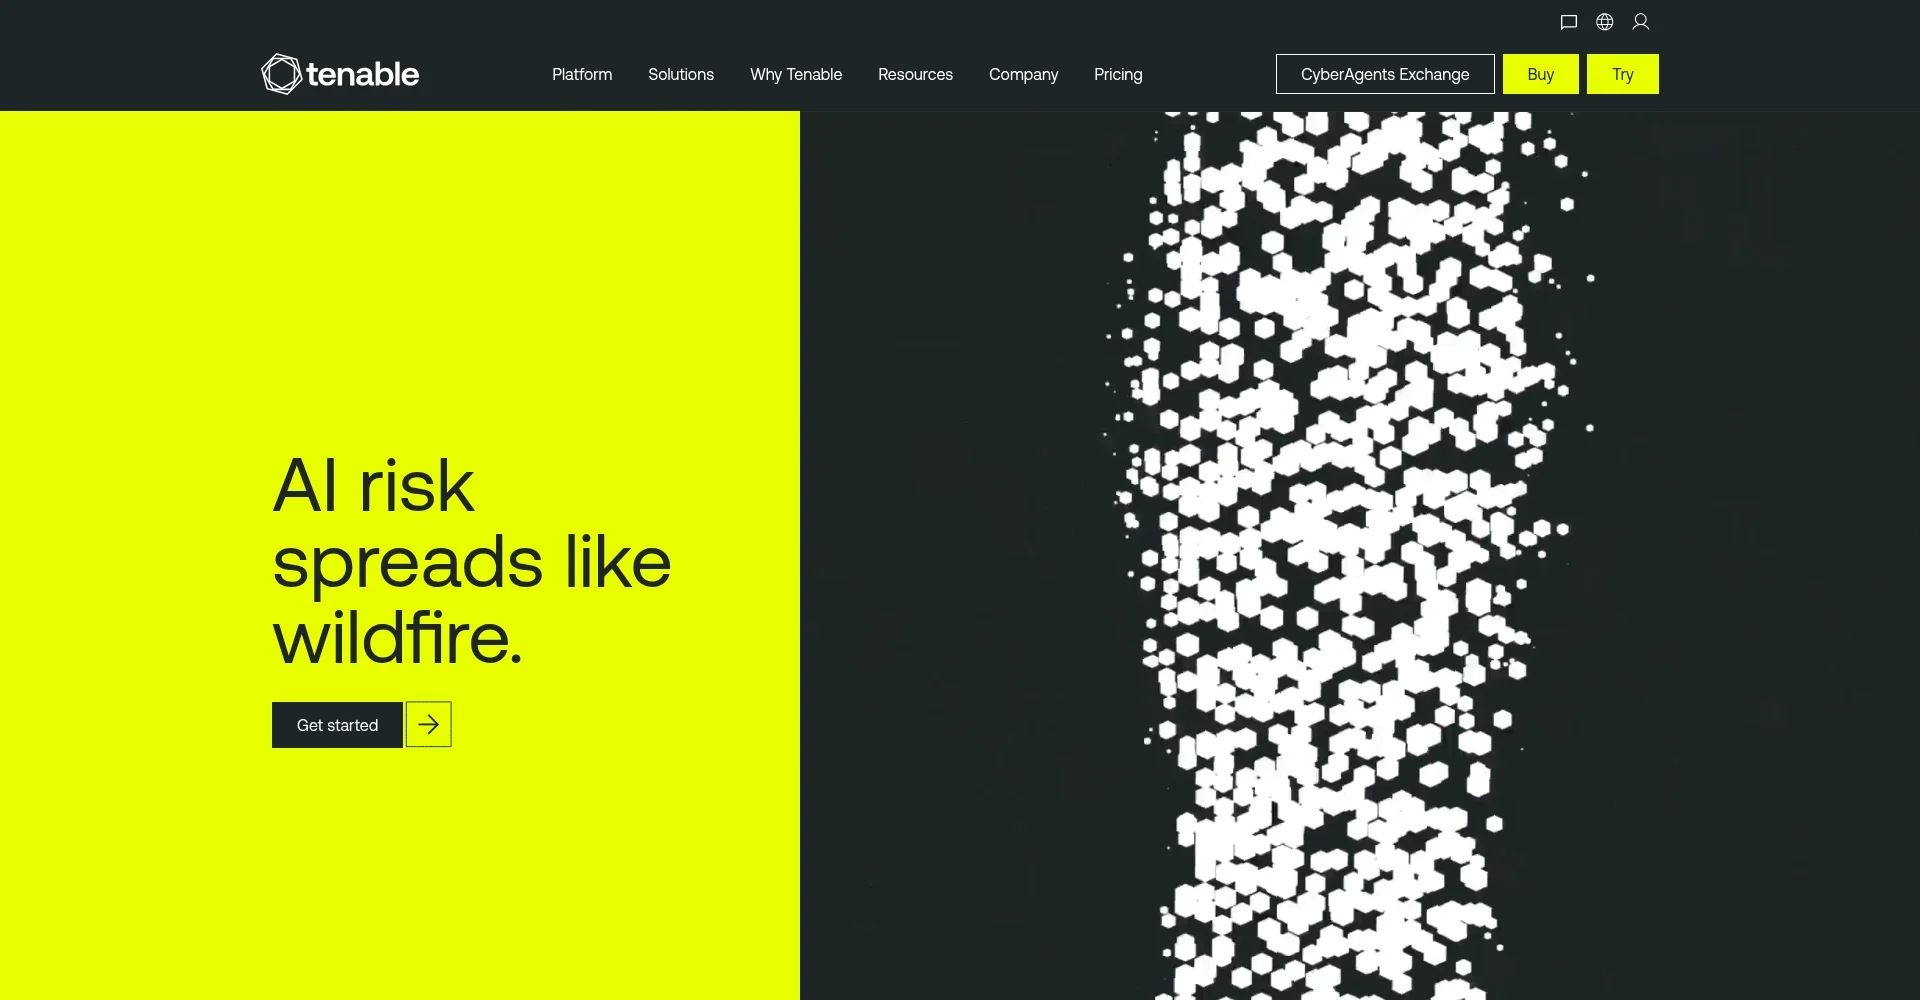
Tenable homepage, captured 3 November 2026 from Germany. The hero headline rotates.
Tenable pricing per asset compared to Vornin's target-based price
Pricing verdict: for 100 hosts and five web apps, Vornin Business costs 34% less (€3,656.44/year) than Tenable One Vulnerability Management plus Web App Scanning, €7,092 against €10,748.44 a year. Tenable licenses every asset, about €44.40 a year each, and sells web apps as a separate licence. Vornin's price also covers code scanning, which Tenable does not offer, and container, Kubernetes cluster and cloud scanning, which Tenable prices on request, so no saving is stated for that coverage.
Platform
Yearly price
Included in this comparison
Business
€7,092
105 targets: 100 hosts and five web apps
Internal and external network and TLS scanning
Web app and API scanning
Attack surface, subdomain, DNS and email scanning
Code, secrets, dependency, infrastructure-as-code, container, Kubernetes and cloud scanning
Named owners, automatic escalation, nine compliance frameworks and an audit evidence pack
Monthly or annual billing
Tenable One Vulnerability Management + Web App Scanning
€10,748.44
100 assets plus five web apps
Internal and external network and TLS scanning
Web app and API scanning on a separate licence
Attack surface scanning on quote; DNS and email in part
No code, dependency or secret scanning
Infrastructure-as-code, container, Kubernetes and cloud scanning on quote
Owner on the linked ticket only; no automatic escalation or audit evidence pack
Compliance frameworks on configuration audits only
Annual prepaid billing only
Tenable Nessus Expert
€6,789.39
One licence for the scanner you install
Internal and external network and TLS scanning
Web app scanning and external attack surface for five domains each per rolling 90 days
DNS and email in part
No code, dependency or secret scanning
Infrastructure-as-code, container, Kubernetes and cloud scanning on quote
No owner on the finding, automatic escalation or audit evidence pack
Compliance frameworks on configuration audits only
Annual prepaid billing only
Tenable Nessus Professional
€4,799
One licence for the scanner you install
Internal and external network and TLS scanning
No web app or API scanning
Attack surface scanning on quote; DNS and email in part
No code, dependency or secret scanning
Infrastructure-as-code, container, Kubernetes and cloud scanning on quote
No owner on the finding, automatic escalation or audit evidence pack
Compliance frameworks on configuration audits only
Annual prepaid billing only
Yearly list prices in euro, excluding VAT, as published to a euro-area visitor. Tenable bills annually, prepaid, and its monthly figures on this page are the annual price divided by 12. Vornin Business, the plan with automatic escalation and the audit evidence pack, is shown on annual billing with each host as its own target. A Vornin target can be an IP range or a cloud account, so hosts in ranges need far fewer targets. Tenable sells container, Kubernetes, cloud configuration and infrastructure-as-code scanning in Tenable One Cloud Exposure, priced on request and not part of the products compared here.
Tenable sells Vulnerability Management online from 100 to 250 assets. With the same five web apps on Web App Scanning, Tenable rises from €895.70/month at 100 hosts to €1,449.87 at 250, computed from its annual price. Vornin Business rises from €591 to €951/month on annual billing, so the gap grows from €304.70 to €498.87 a month.
Monthly cost for 100 to 250 hosts plus five web apps, in euro excluding VAT
Hosts
Vornin Business, annual billing
Tenable One Vulnerability Management + Web App Scanning, annual price divided by 12
100
€591
€895.70
110
€615
€932.37
120
€639
€968.91
130
€663
€1,005.91
140
€687
€1,042.91
150
€711
€1,079.90
160
€735
€1,116.90
170
€759
€1,153.90
180
€783
€1,190.89
190
€807
€1,227.89
200
€831
€1,264.89
210
€855
€1,301.88
220
€879
€1,338.88
230
€903
€1,375.88
240
€927
€1,412.87
250
€951
€1,449.87
Monthly cost for 100 to 250 hosts plus five web apps, excluding VAT. Vornin Business on annual billing versus Tenable One Vulnerability Management plus Web App Scanning, annual prepaid price divided by 12. Tenable sells more than 250 assets on quote only, so the chart stops there. From each vendor's public pricing, verified 6 November 2026.
What you run for the same coverage
Internal and external networks and TLS
Web apps and APIs
Attack surface and subdomains
DNS and email
Code, secrets and dependencies
Infrastructure as code
Containers and Kubernetes
Cloud configuration
Control attestations
Tamper-evident audit evidence
vs
Tenable
Internal and external networks and TLS
Web apps and APIs, on a separate licence
DNS and email, in part
Priced on request with Tenable On quote
Attack surface and subdomains
Infrastructure as code
Containers and Kubernetes
Cloud configuration
Needs another tool with Tenable Not included
Code, secrets and dependencies
Control attestations
Tamper-evident audit evidence
What each extra host adds
Tenable One Vulnerability Management adds about €44.40 a year per asset, about 1.5 times the €28.80 a year (€2.40/month) Vornin Business adds per target above 100 on annual billing, whether it is a host, a web app, an IP range or a cloud account.
Reporting and audit evidence
Tenable maps configuration audits to frameworks and offers NIS2 report templates, but does not map each finding to controls and has no attestations, named sign-off or tamper-evident finding history. Vornin maps each finding to NIS2, DORA and seven more frameworks, records attestations for controls scanning cannot test, and builds an audit evidence pack for a chosen period on Business.
Stack coverage
Vornin Business includes code, dependency, secret, infrastructure-as-code, container, Kubernetes cluster and cloud scanning in the price shown. Tenable prices infrastructure-as-code, container, Kubernetes cluster and cloud scanning on request, and code, dependencies and secrets in code need another tool.
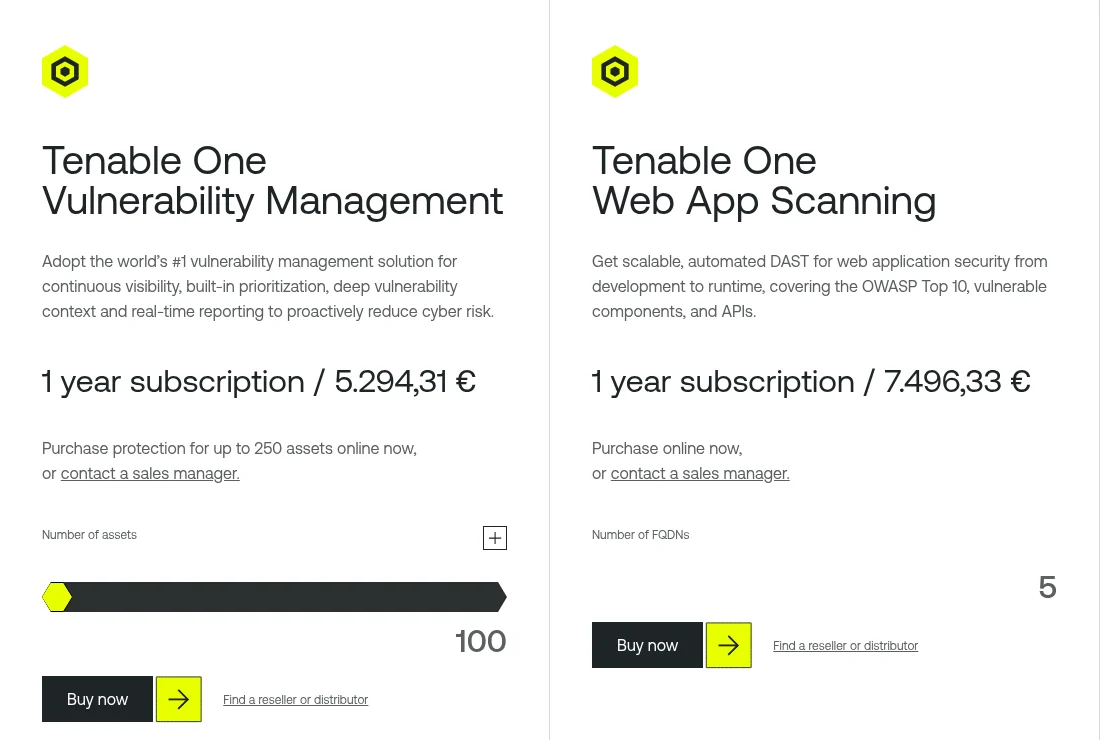
Tenable pricing as shown to a visitor in Germany, captured 3 November 2026. Prices include 19% German VAT: Vulnerability Management €5,294.31 for 100 assets is €4,449 excluding VAT, and Web App Scanning €7,496.33 for five web apps is €6,299.44, together the €10,748.44 a year used above.
Choose Vornin over Tenable for coverage, audit evidence and EU jurisdiction
Bottom line: when you compare Tenable competitors for the best alternative to Tenable, Vornin scans source code, which Tenable does not, and includes the containers and cloud Tenable prices on request. Vornin also lets you assign ownership to each finding, adds auto-escalation and audit evidence, costs 34% less and keeps findings under EU jurisdiction.
Choose if
You want networks, web apps, APIs, code, containers, Kubernetes clusters and cloud in one subscription. Vornin covers 100 hosts and five web apps for €7,092 a year, 34% less than Tenable One Vulnerability Management plus Web App Scanning at €10,748.44, which scans networks and web apps only.
You need evidence for a NIS2, DORA or ISO 27001 audit, such as each finding mapped to controls, attestations for the controls scanning cannot test, and named sign-off in one tamper-evident record.
You need to assign ownership to each finding, with SLA deadlines, auto-escalation and notifications by email and webhook, and tickets in GitHub, GitLab, Azure DevOps or Jira.
You want monthly billing, or a price that counts an IP range or a cloud account as one target. Tenable bills every product annually, prepaid, and licenses each asset.
Your findings must stay under EU jurisdiction, with hosting and AI on EU providers and a vendor with no US office or parent.
Tenable's scan coverage, remediation, compliance evidence and jurisdiction compared to Vornin
Bottom line: Tenable does not scan code, dependencies or secrets in code, prices ASM, infrastructure as code, container images, Kubernetes clusters and cloud configuration on request, and licenses web app and API scanning separately. Vornin covers all of them in one subscription. Beyond scanning, Tenable puts the owner on the linked ticket rather than the finding, does not escalate a missed deadline, keeps no tamper-evident history and holds data with a US company on US-owned AWS, which exposes it to the US CLOUD Act. Vornin lets you assign ownership to each finding, adds SLA deadlines with auto-escalation and notifications, and maps each finding to NIS2 and DORA controls with a tamper-evident history, under EU jurisdiction.
vs
Tenable
External
Vornin
Subdomains
Network and exposed services
Web apps
APIs
TLS
DNS and email
Tenable
Nessus or VM
Base product
Network and exposed services
TLS
DNS and email (partial)
Web App Scanning
Add-on
Web apps (add-on)
APIs (add-on)
Attack Surface Management
Add-on, on quote
Subdomains (add-on, on quote)
Code and cloud
Vornin
Source code (SAST)
Dependencies (SCA)
Secrets in code
Infrastructure as code
Containers
Kubernetes clusters
Cloud configuration
Tenable
Cloud Exposure
Add-on, on quote
Infrastructure as code (add-on, on quote)
Containers (add-on, on quote)
Kubernetes clusters (add-on, on quote)
Cloud configuration (add-on, on quote)
No coverage for
Source code (SAST) (not included)
Dependencies (SCA) (not included)
Secrets in code (not included)
Internal
Vornin
Internal networks
Tenable
Nessus or VM
Base product
Internal networks
Capability
Tenable
Scanning
Attack-surface monitoring
Yes
Yes, on quote; five domains per rolling 90 days on Nessus Expert
Subdomain discovery
Yes
Yes, on quote; five domains per rolling 90 days on Nessus Expert
Subdomain takeover checks
Yes
Yes, with web app scanning (Web App Scanning or Nessus Expert)
External network and exposed services
Yes
Yes
Internal network scanning
Yes
Yes
Web application scanning
Yes
Yes, on a separate licence: Web App Scanning, or Nessus Expert for five web apps per rolling 90 days
Authenticated web app scans
Yes
Yes, on a separate licence
API scanning
Yes
Yes, on a separate Web App Scanning licence
TLS
Yes
Yes
DNS and email security
Yes
Partial: Microsoft 365 configuration audits; record inventory on quote
Risk acceptance with a review date that reopens the finding
Yes
Yes
Fix verified by rescan, auto-close
Yes
Yes
Reopen on recurrence
Yes
Yes
Findings deduplicated across scanners
Yes
Partial: assets counted once; no finding merge across scanners
Jira tickets
Yes
Yes
GitHub, GitLab or Azure DevOps tickets
Yes
No
Reporting and compliance evidence
PDF reports and CSV exports
Yes
Yes
NIS2 and DORA reports
Yes
Partial: NIS2 report templates; DORA guidance study only
Findings mapped to compliance controls
Yes, nine frameworks, including NIS2, DORA and ISO 27001
Partial: configuration audits and guidance studies only
DORA scored by the regime that applies (standard or simplified)
Yes
No
Manual attestations for controls scanning cannot test
Yes
No
Named, expiring sign-off on audit evidence
Yes
No
Tamper-evident finding history
Yes
No
Auditor evidence pack
Yes, scoped to an audit period
No
Jurisdiction and data residency
Company with no US office or parent
Yes
No: US company Tenable, Inc.
Data stored in the EU
Yes
Yes, Frankfurt region on US-owned AWS
Hosting with an EU provider
Yes
No: US-owned AWS
AI processing on EU providers
Yes, Scaleway (France), with credentials masked
No: Tenable's AI, Hexa AI, needs a Tenable One quote and runs on US-owned Amazon Bedrock
Scan results and customer findings outside US CLOUD Act reach
Yes
No: US company on US-owned AWS
Pricing
Monthly billing
Yes
No: annual prepaid only
Web apps in the same licence as hosts
Yes
Yes, on quote; published prices need a separate Web App Scanning licence
YesNoPartial
Nessus Professional, Nessus Expert, Tenable One Vulnerability Management and Tenable One Web App Scanning have published prices. "On quote" marks a capability sold only in a quote-only product, such as Tenable One Foundation or Advanced, Tenable One Cloud Exposure or Attack Surface Management. Feature access varies by subscription.
How Tenable and Vornin differ on coverage, audit evidence, fix tracking and jurisdiction
Bottom line: Tenable does not scan code, prices containers and cloud on request, keeps no tamper-evident evidence, does not escalate a missed deadline and holds data with a US company on US-owned AWS. Vornin scans code, containers and cloud in one subscription, maps each finding to controls with tamper-evident evidence, escalates missed deadlines and keeps findings under EU jurisdiction.
Coverage in one subscription
Network, TLS, web application and API scanning: Yes
Attack-surface monitoring: Yes
DNS and email security: Yes
Code, dependency and secrets in code scanning: Yes
Infrastructure-as-code, container image, Kubernetes cluster and cloud configuration scanning: Yes
vs
Tenable
Network, TLS, web application and API scanning: Yes; web apps and APIs on a separate licence
Attack-surface monitoring: Yes, on quote
DNS and email security: Partial, Microsoft 365 audits; record inventory on quote
Code, dependency and secrets in code scanning: No
Infrastructure-as-code, container image, Kubernetes cluster and cloud configuration scanning: Yes, on quote
Coverage verdict: Vornin includes all of these surfaces in one subscription with a published price. Tenable licenses web apps and APIs separately, prices ASM, infrastructure as code, container images, Kubernetes clusters and cloud configuration on request, covers DNS and email security in part, and does not scan source code, dependencies or secrets in code.
Evidence you can hand an auditor
Findings mapped to compliance controls: Yes, nine frameworks
Manual attestations: Yes
Named, expiring sign-off on audit evidence: Yes
Tamper-evident finding history: Yes
Auditor evidence pack: Yes, scoped to an audit period
vs
Tenable
Findings mapped to compliance controls: Partial, configuration audits and guidance studies only
Manual attestations: No
Named, expiring sign-off on audit evidence: No
Tamper-evident finding history: No
Auditor evidence pack: No
Compliance verdict: Vornin maps each finding to the relevant controls across nine frameworks, records attestations for the controls scanning cannot test, and keeps the evidence tamper-evident with named sign-off. Tenable maps configuration audits to frameworks and publishes guidance studies for NIS2 and DORA, but offers no per-finding control mapping, attestations, named sign-off or tamper-evident finding history.
Owners, deadlines and escalation
Named owner per finding: Yes
Per-severity SLA deadlines: Yes
Automatic escalation by email and webhook: Yes
Risk acceptance with a required reason: Yes
GitHub, GitLab or Azure DevOps tickets: Yes
vs
Tenable
Named owner per finding: Partial, on the linked ticket
Risk acceptance with a required reason: Partial, comment optional
GitHub, GitLab or Azure DevOps tickets: No
Remediation verdict: Vornin lets you assign ownership to each finding, escalates a missed deadline by email and webhook, requires a reason for every accepted risk and opens tickets in GitHub, GitLab, Azure DevOps or Jira. Tenable puts the owner on the linked ticket rather than the finding, shows SLA deadlines in a dashboard widget, does not escalate and does not open tickets in GitHub, GitLab or Azure DevOps.
EU jurisdiction and data residency
EU company: Yes
No US office or parent: Yes
Data stored in the EU: Yes
Hosting: Yes, German-owned Hetzner
AI processing: Yes, EU provider
vs
Tenable
EU company: No, US company Tenable, Inc.
No US office or parent: No
Data stored in the EU: Yes, Frankfurt region
Hosting: No, US-owned AWS
AI processing: No, Hexa AI on US-owned Amazon Bedrock, Tenable One quote only
Jurisdiction verdict: data location is not jurisdiction. Tenable can store EU data in its Frankfurt region, but on US-owned AWS, and EU customers contract with a European Tenable subsidiary, owned by the US parent Tenable, Inc. Data held by US providers is exposed to the US CLOUD Act. Tenable's privacy policy says: "In certain situations, Tenable may be required to disclose personal data in response to lawful requests by public authorities, including to meet national security or law enforcement requirements." Vornin hosts on German-owned Hetzner, and all scan data, AI included, stays in the EU.
Hand your auditor evidence for each control
Vornin maps every finding to your NIS2, DORA and ISO 27001 controls and keeps the history tamper-evident.
Yes. Vornin scans networks and web apps like Tenable, plus source code, and includes the containers and cloud Tenable prices on request. Compared to Tenable, Vornin also lets you assign ownership to each finding, adds SLA deadlines with auto-escalation and notifications, and maps each finding to NIS2, DORA and seven more frameworks. Vornin costs 34% less for 100 hosts and five web apps and keeps findings under EU jurisdiction.
What is the main difference between Vornin and Tenable?
Coverage in one subscription. Tenable sells network scanning in Nessus and Tenable One Vulnerability Management, web app scanning on a separate licence, and containers, Kubernetes clusters and cloud on quote, and it does not scan source code. Vornin covers all of them in one plan. Compared to Tenable, Vornin also keeps the named owner on the finding rather than the ticket, escalates a missed deadline by email and webhook, and keeps a tamper-evident finding history with an auditor evidence pack. Tenable does not escalate a missed deadline or keep a tamper-evident finding history.
What is a Nessus alternative that covers web apps, code and cloud in one subscription?
Vornin scans internal and external networks like Nessus and adds web apps, APIs, source code, dependencies, secrets, infrastructure as code, container images, Kubernetes clusters and cloud configuration in the same subscription. Nessus Professional, at €4,799 a year, scans networks only. Nessus Expert, at €6,789.39 a year, adds web apps and external attack surface for five domains each per rolling 90 days. Neither scans code, containers or cloud.
How does Tenable pricing compare in Europe?
Vornin costs 34% less for the same mix. Tenable One Vulnerability Management for 100 assets plus Web App Scanning for five web apps costs €10,748.44 a year excluding VAT, prepaid, as published to a euro-area visitor. Vornin covers the same 100 hosts and five web apps for €7,092 a year and also includes code, container and cloud scanning. Tenable prices containers and cloud on request, bills annually only and sells more than 250 assets on quote. Nessus Professional costs €4,799 a year and scans networks only.
Is Tenable's data exposed to the US CLOUD Act?
Yes. Tenable, Inc. is a US company and hosts customer data on US-owned AWS, which exposes that data to the US CLOUD Act, even when it is stored in Tenable's Frankfurt region. EU customers contract with a European Tenable subsidiary, owned by Tenable, Inc. Vornin is a European company with no US office or parent, and hosts scan results and customer findings with EU providers, AI included.
Can I import my Nessus scan results into Vornin?
Yes. Vornin imports Nessus XML, as well as OpenVAS XML, CSV and JSON, so findings from your existing Nessus scans move into one remediation and evidence workflow while you switch.